CDN resource
To deliver your content, the CDN needs to know where to get the files and how to handle requests. This information is configured in a CDN resource, which can serve one or more domains. A resource has one main domain and can have additional ones. All of them share the same settings, so domains that need different settings are separate resources. Each resource uses an origin group to specify where files come from. An origin group can contain one or more origins, such as servers, storage buckets, or FastEdge HTTP applications.Cache
When an edge server retrieves a file from the origin, it can keep a copy in its cache for future requests. Whether the file can be cached depends on the HTTP status code and theCache-Control header of the response.
The copy does not stay in the cache forever. How long it stays is set by the cache lifetime, which comes from the origin headers or from the CDN resource settings.
Origin shielding
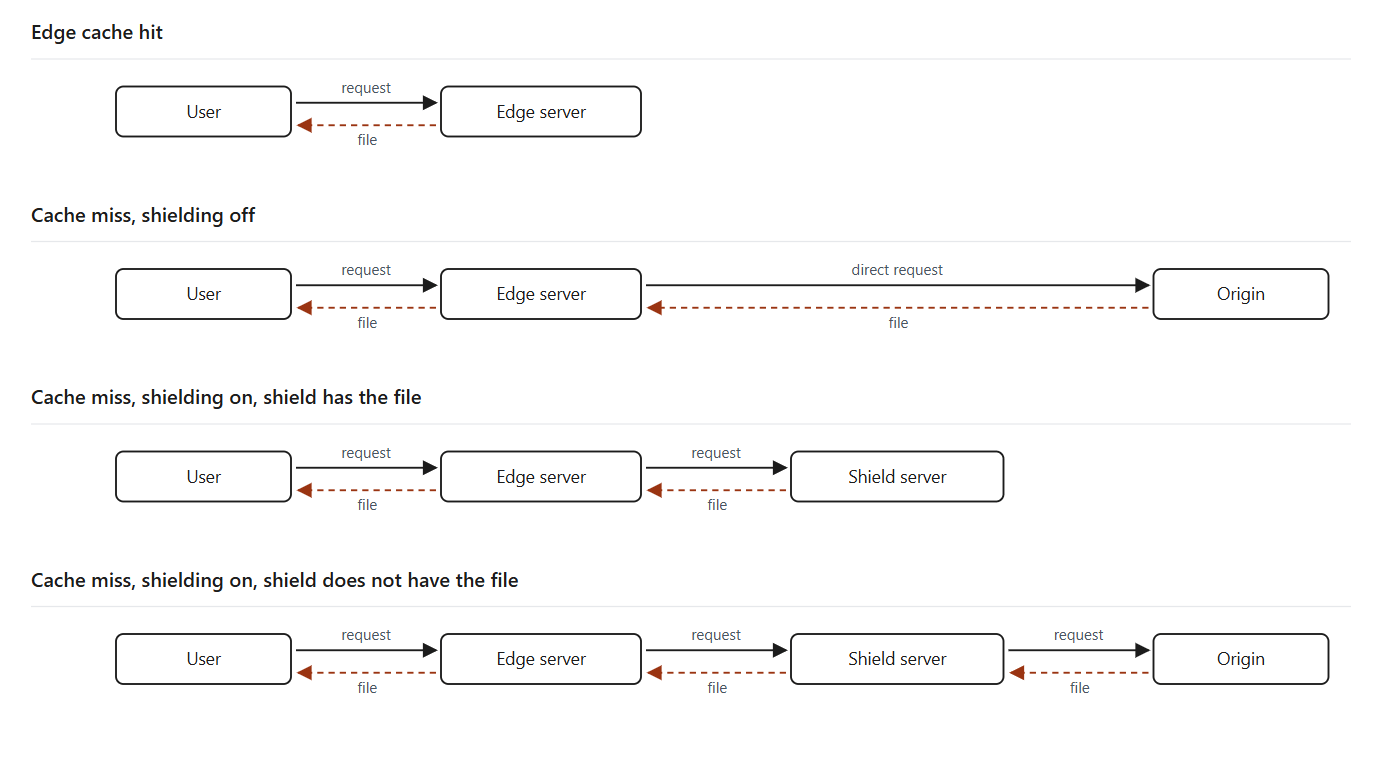
The cache reduces the number of requests to the origin, but not to zero: a file that is not cached yet, or whose copy has expired, is requested again. If this happens often on many edge servers, the origin can be overloaded with requests. You can reduce this load with Origin Shielding, which adds a shield server: another cache between the edge servers and the origin. Edge servers request missing files from the shield server first. If the file is not there either, the shield server retrieves it from the origin.The complete delivery path
A request reaches the nearest edge server. If that server has the file, it sends the file and does not contact the origin. If it does not, it requests the file from the origin. With Origin Shielding enabled, the edge server requests the file from the shield server, and the shield server contacts the origin only when it does not have the file. Each row is a separate request.